
NAID AAA Certification: The Data Destruction Standard Explained
Explore NAID AAA certification, the leading standard for data destruction, and understand its importance in ensuring secure data handling practices.
Introduction
NAID certification is the global benchmark for verifying that data destruction providers meet rigorous operational and security standards. The certificate of data destruction is the operator's primary documentary defense in a post-incident regulatory review. It is also, in our review of vendor profiles across the ITAD landscape, the document with the highest variance in what it actually means. When a vendor claims NAID certification, the underlying question is not whether they hold the credential — it is whether the certification's operational requirements match the risk profile of the assets being destroyed.
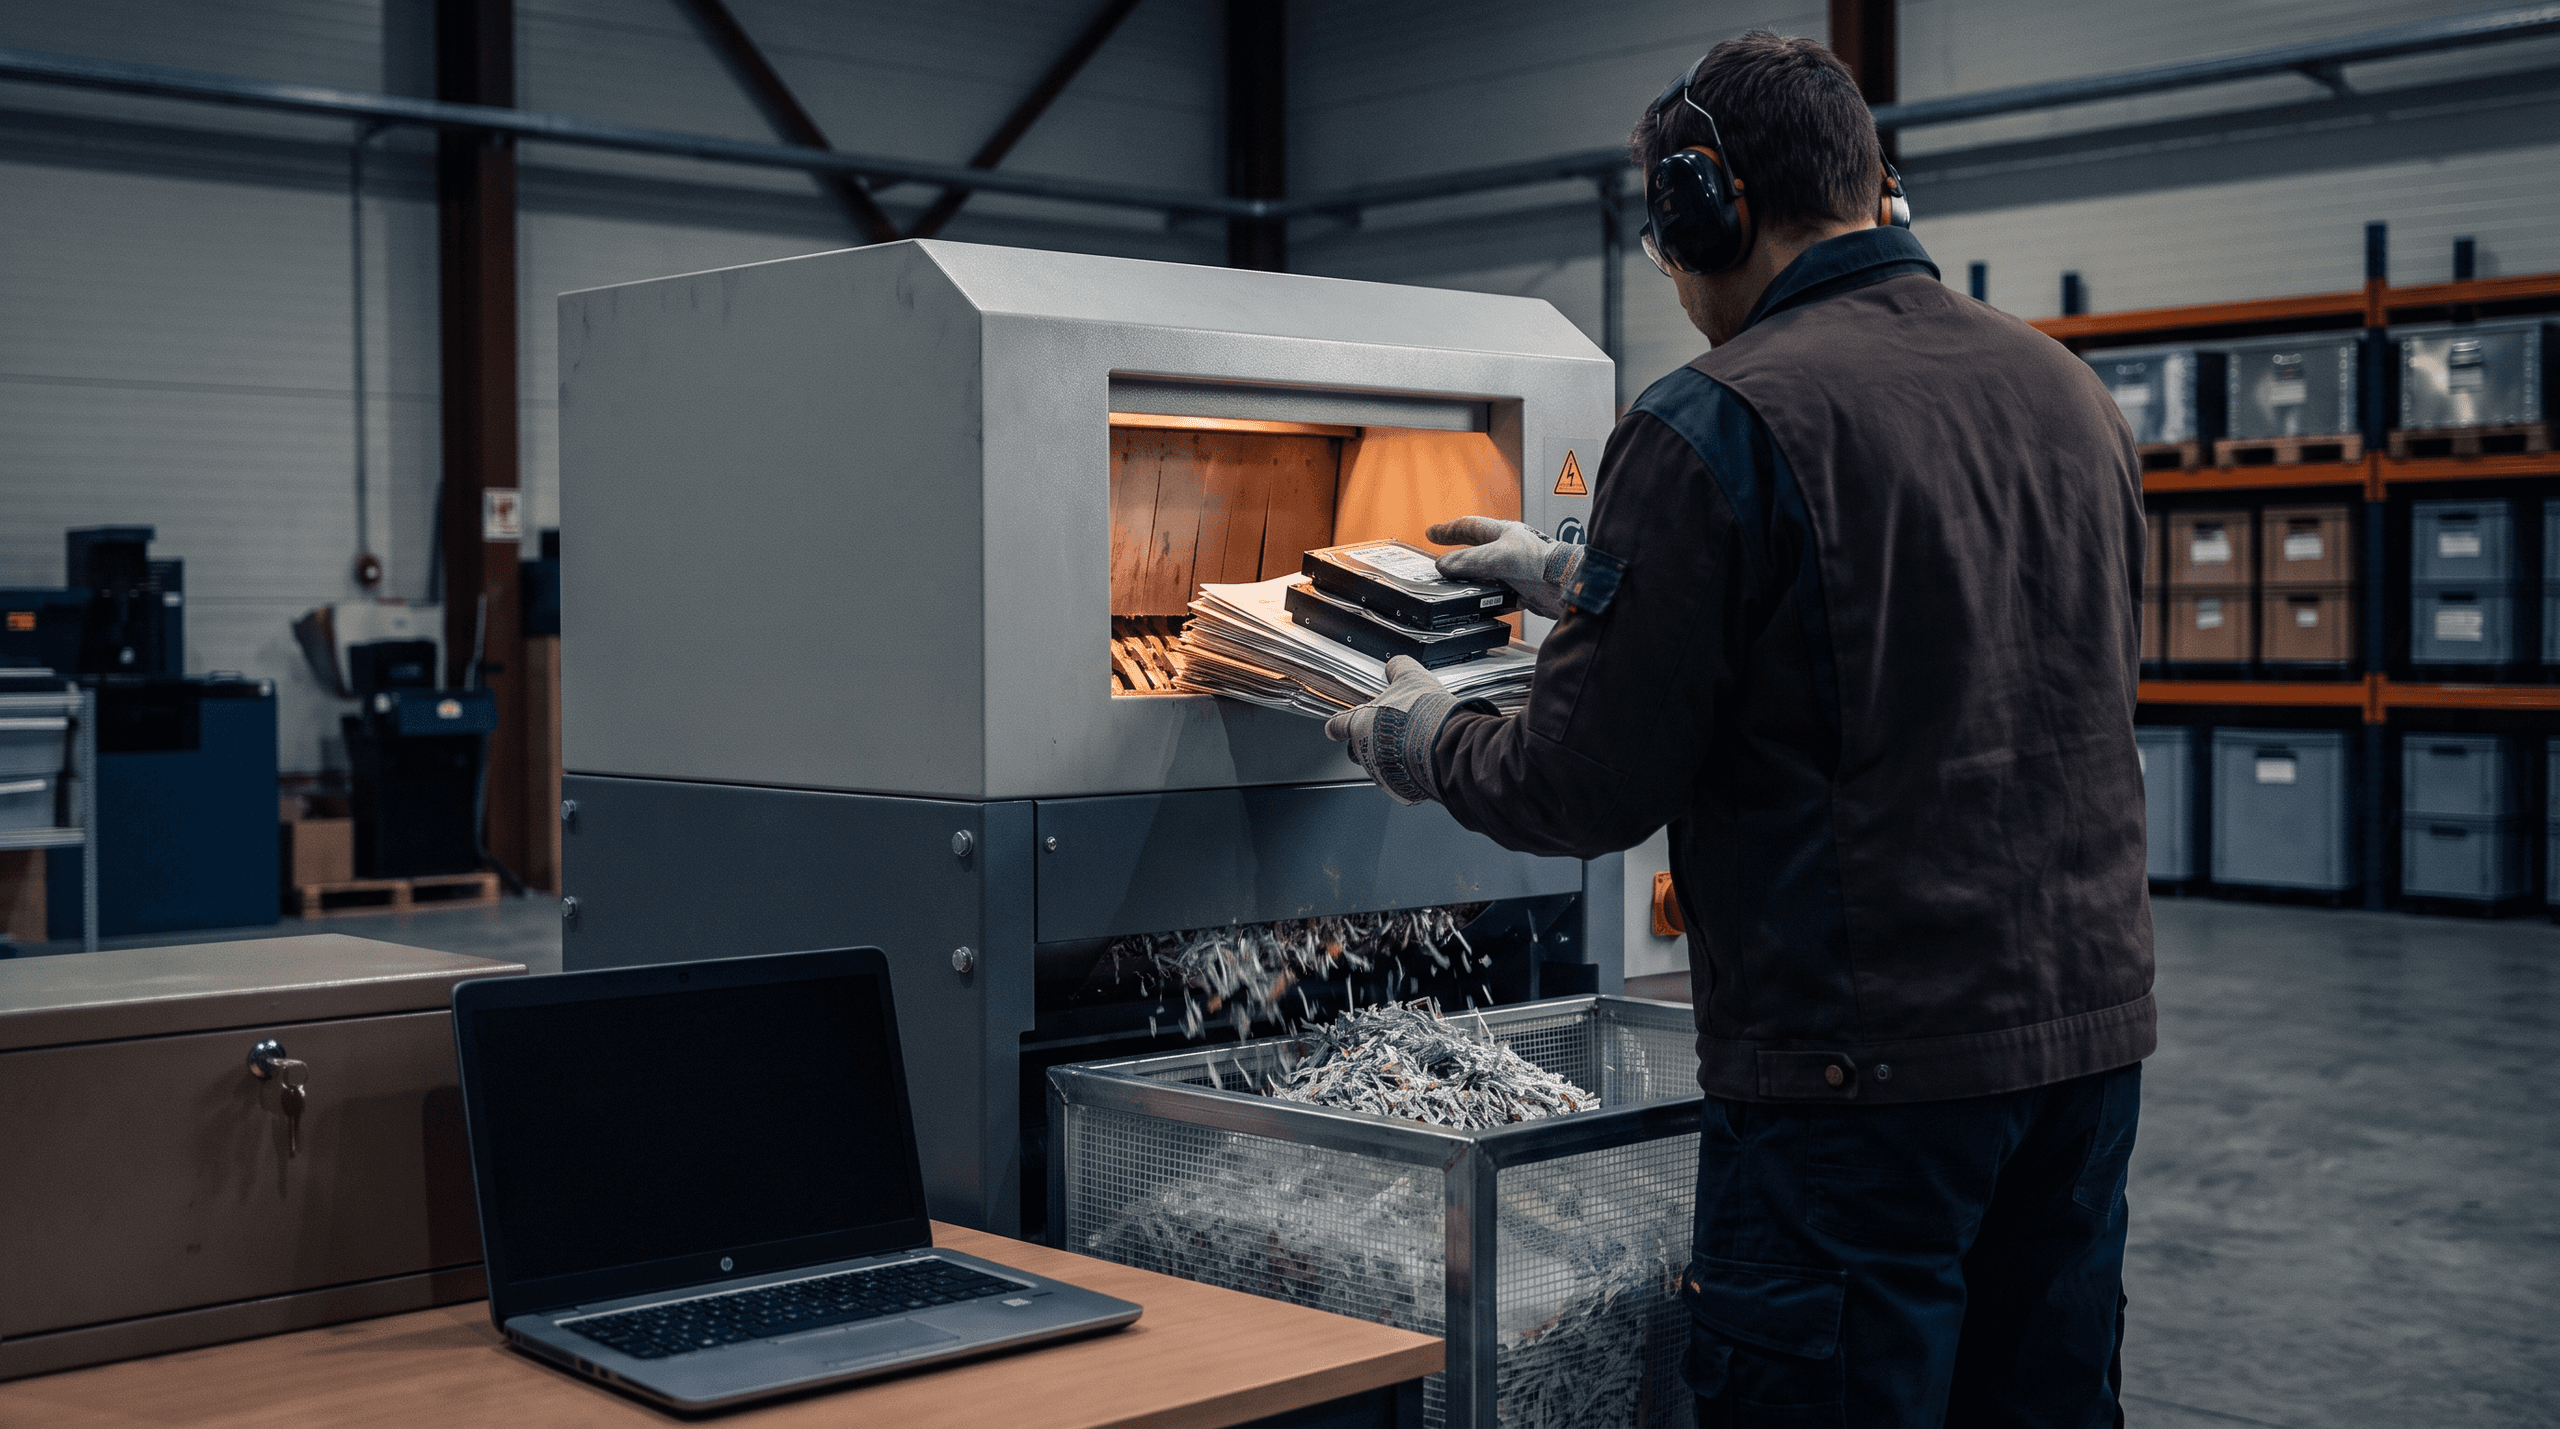
NAID certification sets the standard for secure information destruction through a rigorous audit program that includes both scheduled and unannounced reviews. The certification applies to physical destruction of paper records and electronic media destruction of hard drives and other storage devices. Endorsements further define the scope: mobile operations that perform on-site destruction, facility-based operations that process material at a central location, and specific media types that determine which destruction methods apply.
For enterprise IT and procurement teams, the certification addresses a structural problem in vendor selection. Without a third-party verification standard, the buyer must independently verify chain-of-custody controls, employee screening protocols, and destruction method adequacy. NAID certification shifts that burden to an independent auditor who verifies compliance against published specifications. The certification does not eliminate the buyer's due diligence requirement — it establishes a baseline that the vendor's documented procedures match the operational reality an auditor observes.
The certification's value is in what survives audit. When a regulatory review or civil discovery process demands proof that sensitive data was destroyed according to a documented standard, the NAID-certified vendor's paper trail includes not only the certificate of destruction but also the underlying audit record that verifies the vendor's procedures were followed. For a detailed comparison of how NAID certification fits within the broader certification landscape, see ITAD Certifications: What R2v3, NAID AAA and e-Stewards Cover.
This guide walks through the operational requirements, audit mechanics, and common implementation gaps that determine whether NAID certification translates to audit-defensible data destruction in practice.
Prerequisites
Before evaluating NAID certification in the context of vendor selection or internal audit preparation, you need a working understanding of the underlying data destruction landscape. The certification is not a standalone compliance checkbox — it sits on top of operational controls, regulatory obligations, and documented chain-of-custody mechanics that must already be in place.
Foundational Knowledge Requirements
You should understand the distinction between physical destruction (shredding, crushing, degaussing) and logical sanitization (NIST 800-88 overwrite methods, cryptographic erasure). NAID certification applies to both domains, but the verification process and the documentary trail differ materially. If your organization processes electronic media for reuse, you need to know what "100% of a device's physical memory locations" means in practice — and what happens when that verification step fails.
You should also be familiar with the major regulatory frameworks that drive data destruction requirements: FACTA, HIPAA, PCI DSS, and GDPR where applicable. NAID certification is positioned as a mechanism to support compliance with these regimes, but the certification itself does not replace the underlying legal obligation. The auditor will ask whether your vendor's certification maps to the specific control language in your regulatory framework.
Operational Context
You need a baseline understanding of what an unannounced audit entails. NAID certification includes both scheduled and unannounced reviews, and the unannounced component is the mechanism that separates certification from self-attestation. If your vendor selection process does not account for the difference between a vendor who passed a scheduled audit and one who maintains controls that survive unannounced review, you are not positioned to evaluate the certification's value.
Finally, you should understand the role of chain-of-custody documentation in a post-incident review. The certificate of data destruction is the operator's primary documentary defense, and NAID certification sets operational standards for how that certificate is generated, what it must contain, and how the underlying process is verified. If you do not know what your auditor will accept as proof of destruction, the certification's relevance to your risk posture remains unclear.
For a broader view of how NAID certification fits alongside other industry credentials, see ITAD Certifications: What R2v3, NAID AAA and e-Stewards Cover.
How Does NAID Certification Work?
NAID certification is a structured program administered by i-SIGMA, and it operates through a defined set of requirements, endorsements, and audit cycles. The following steps break down how the certification works, what it covers, and what an operator must maintain to hold the credential.
Step 1
Understand the certification scope
NAID certification applies to both physical destruction (paper, hard drives, optical media) and electronic media destruction (data-bearing devices). The program uses endorsements to define the service model — mobile (on-site destruction), facility-based operations, or a combination of both. An operator selects the endorsements that match their operational posture, and the auditor verifies compliance against those specific categories.
Step 2
Review operational requirements
Certification requires strict adherence to documented procedures covering employee screening, CCTV retention, secure handling protocols, and chain-of-custody documentation. The i-SIGMA Certification Specifications Manual contains the full requirements matrix. Operators must implement security measures that protect confidential material from intake through final destruction, and those measures must be documented in a way that survives audit.
Step 3
Prepare for scheduled and unannounced audits
NAID certification includes both scheduled and unannounced reviews. The scheduled audit verifies that documented procedures match operational reality. The unannounced audit tests whether those procedures hold under normal operating conditions. In our editorial review of vendor profiles, operators who maintain certification consistently describe the unannounced audit as the more rigorous test — it reveals whether the documented process is the actual process or a parallel artifact maintained for compliance theater.
Step 4
Verify data sanitization and destruction processes
For devices going to reuse, the operator must verify that prescribed overwrite instructions have been successfully executed for 100% of a device's physical memory locations. For devices going to destruction, the operator must validate that physical destruction processes render data unrecoverable. The verification requirement is not a sampling protocol — it is a 100% requirement. Every device, every time.
Step 5
Align certification with regulatory compliance
NAID certification supports compliance with FACTA, HIPAA, and PCI DSS, among other frameworks. The certification does not replace a compliance program, but it provides documented evidence that the destruction process meets a published standard. In regulatory review, the question the auditor will ask is whether the operator's documented process aligns with the regulatory requirement — NAID certification provides a defensible answer to that question.
Understanding Endorsements and Service Models
NAID certification uses endorsements to distinguish between service models and media types. An operator may hold certification for mobile shredding of paper but not for facility-based hard drive destruction. The endorsement structure allows an operator to certify only the services they actually provide, rather than carrying a blanket credential that implies capabilities they do not maintain.
For enterprise IT teams evaluating vendors, the endorsement detail matters. A vendor with NAID certification for mobile paper shredding is not certified for hard drive destruction unless the endorsement explicitly covers electronic media. The certification is modular, and the modules must match the scope of work. For a detailed comparison of how NAID certification fits alongside other industry credentials, see ITAD Certifications: What R2v3, NAID AAA and e-Stewards Cover.
The endorsement structure allows an operator to certify only the services they actually provide, rather than carrying a blanket credential that implies capabilities they do not maintain.
The Role of i-SIGMA in Certification Administration
i-SIGMA administers the NAID certification program, manages the audit schedule, and maintains the certification specifications manual. The organization operates as the certification body, and certified operators are subject to i-SIGMA's audit protocols and compliance requirements. The certification is not self-attested — it requires third-party verification through the i-SIGMA audit process.
In the operator's defense, i-SIGMA's audit structure provides a documented trail that holds up in regulatory review. The certification is not a marketing credential — it is an operational posture verified by an independent body through scheduled and unannounced audits.
What Are Common NAID Certification Compliance Gaps?
The certification process surfaces predictable failure modes. Most operators encounter the same three: incomplete sanitization verification, mobile-environment documentation gaps, and downstream responsibility ambiguity. These are not edge cases — they are the structural weak points where audit-defensible practice diverges from what the operator believes is happening.
Verification Gaps in Sanitization Processes
The standard requires verification of successful sanitization for 100% of a device's physical memory locations when devices go to reuse. In practice, operators run overwrite tools that report completion, then treat the report as verification. The auditor's question is different: How do you prove the prescribed overwrite instructions executed successfully across the entire physical address space?
For devices going to destruction, the requirement shifts to validating that the physical destruction process itself prevents data recovery. The operator must demonstrate that shredding, crushing, or degaussing achieved the documented outcome — not just that the device entered the destruction process.
Mobile Sanitization and Documentation Requirements
Organizations can sanitize data storage devices in mobile environments — vehicles, temporary facilities, customer sites — provided the vehicle and processes meet the same data-security requirements as fixed facilities. The failure mode: operators deploy mobile units without documenting that the mobile environment satisfies the underlying control structure.
The chain-of-custody question becomes sharper in mobile contexts. When a device leaves the customer site in a vehicle, the documentary record must show continuous control from pickup through sanitization completion. If sanitization happens in the vehicle, the operator must prove the mobile environment met facility-grade security controls at the moment of sanitization.
Responsibility for Downstream Data Security
Organizations retain responsibility for preventing unauthorized access to customer data, regardless of the data-bearing devices' final disposition. This creates a structural problem when operators subcontract downstream processing: the responsibility does not transfer with the asset.
In tolling arrangements — where the customer retains ownership and the operator performs processing services — the operator must inform the customer that data sanitization remains the customer's responsibility. In all other cases, the operator owns the outcome. If a downstream processor fails to sanitize before releasing a device, the upstream operator carries the liability.
The contract language must be explicit. General indemnification clauses do not satisfy the standard's requirement that the organization ensure effective sanitization prior to the device's departure from the organization's control. "Control" in this context means documented custody, not legal ownership. For more on how certificates of destruction document this chain of custody, see Data Destruction Certificate: Key Elements and Auditor Expectations.
Certification Scope and Multi-Facility Operations
NAID certification applies per facility, not per organization. An operator with three processing centers must certify each location independently. The common mistake: assuming corporate-level certification covers all sites, then discovering during audit that only the headquarters facility holds the credential.
For more context on how ITAD certifications layer together in multi-facility operations, see the full certification landscape breakdown.
Multi-facility operators face a second challenge: maintaining consistent sanitization processes across locations while documenting site-specific validation. The standard does not permit averaging verification rates across facilities or treating one site's successful audit as evidence for another.
Conclusion
NAID certification remains the most recognized verification of data destruction qualifications in the world. It addresses the documentary and operational requirements that regulators, auditors, and enterprise IT teams expect when evaluating a vendor's posture. The certification's dual-audit structure—scheduled and unannounced—creates the accountability mechanism that survives regulatory review.
For organizations handling data subject to FACTA, HIPAA, PCI, or equivalent frameworks, NAID certification provides the documented safeguards that hold up in audit. The certification applies to both physical destruction and electronic media destruction, with endorsements covering mobile (on-site) operations, facility-based processing, and specific media types including paper and hard drives. This scope ensures that the certification aligns with the full range of data destruction methods enterprise IT teams deploy.
The operational standards underneath the certification—CCTV retention, employee screening, documented procedures for confidential material—are the controls that define the vendor's actual security posture. When a vendor claims NAID certification, the question is not whether the certificate exists, but whether the underlying controls match the scope of your engagement. In our editorial review of vendor profiles, the gap between the certificate and the practiced control is where the risk lives.
For enterprise IT and procurement leads building an ITAD vendor selection process, NAID certification is a necessary credential but not a sufficient one. The certification verifies that the vendor meets a baseline standard; it does not verify the vendor's downstream chain-of-custody, contract language, or the documentary record they produce per engagement. Those elements require additional evaluation, and the ITAD certifications landscape provides the broader context for how NAID certification fits alongside R2v3, e-Stewards, and NIST 800-88 in a complete vendor assessment.
The certification gives clients confidence that proper safeguards are in place for secure handling, transportation, and final destruction of data. That confidence is audit-defensible when the vendor's documented procedures match their practiced controls and when the certificate of data destruction they issue reflects the scope of work actually performed. In the operator's defense, the certification is a meaningful signal—but the question the auditor will ask is whether the vendor's posture held up in practice, not whether the certificate was framed on the wall.
FAQ
What is NAID certification?NAID certification is a third-party verification standard for data destruction providers, administered by i-SIGMA, that confirms operators meet rigorous operational, security, and documentation requirements through scheduled and unannounced audits.
Does NAID certification cover both paper and electronic media?Yes. NAID certification applies to physical destruction of paper records and electronic media destruction of hard drives and storage devices, with specific endorsements defining which service models and media types are covered.
How often are NAID-certified operators audited?NAID certification requires both scheduled and unannounced audits. The unannounced component ensures that documented procedures reflect actual operational practice, not just compliance artifacts.
Is NAID certification required for regulatory compliance?NAID certification is not legally required, but it provides documented evidence that destruction processes meet published standards, supporting compliance with FACTA, HIPAA, PCI DSS, and similar frameworks.